


A certification can tell people what you studied. A thoughtful AI governance portfolio can show how you think when a real decision has trade-offs, missing information, and someone who must own the outcome.
For GRC, privacy, security, product, data, UX, policy, and technical professionals building a visible, trustworthy path into AI governance.
There is a familiar trap in a fast-growing field: learn the acronym, collect the framework, update the headline, and call yourself an expert. AI governance makes that trap especially tempting. The language sounds authoritative—risk, safety, assurance, responsible AI, compliance—but the work only becomes credible when it helps a team decide what to do, who owns the decision, and what happens when conditions change.
That is why an AI governance portfolio is more useful than a folder of certificates or a stream of broad opinions. It gives people something much rarer: evidence of judgment. Not proof that you have governed a global production system if you have not. Proof that you can take a bounded AI scenario, identify the important questions, make your assumptions visible, and turn principles into a reviewable plan.
This distinction matters for career switchers, but it also matters for experienced practitioners. A security leader, privacy professional, product manager, researcher, or data scientist may already have relevant judgment. The portfolio is how you translate that judgment into an AI-governance language that a hiring manager, collaborator, client, or conference organizer can understand.
The personal-brand move: do not publish a claim such as “I am an AI governance expert.” Publish a small body of work that lets a reader reach that conclusion—or see exactly where you are still learning.
Why framework fluency is not yet public proof
Frameworks matter. The NIST AI Risk Management Framework, the OECD AI Principles, and other standards give teams useful language for trustworthy AI. But a framework is a map, not a decision. Two people can quote the same principle and produce very different work when they have to name the system owner, define a harm, choose a control, or explain a residual risk to a nontechnical leader.
Your portfolio should therefore show translation. It should move from a vague statement—“be transparent”—to a specific question: transparent to whom, about what, at which point in the workflow, and with which evidence? It should move from “human oversight” to a visible intervention path: who can pause the system, what triggers review, and what gets recorded after an incident?
In a credible portfolio, uncertainty is not an embarrassment to hide. It is part of the work product.
That makes the portfolio a better personal-brand asset than polished hot takes. It shows a recognizable professional habit: you do not confuse a principle with an implementation, a vendor claim with verification, or a scenario exercise with operational experience.
Choose one scenario you can explain end to end
Start smaller than your ambition. Pick a realistic but safe fictional scenario, a public-interest case, or a sanitized version of a problem you understand. The best scenario is narrow enough to explain in one sentence and rich enough to raise real governance questions.
For example: a mid-sized university wants an AI assistant to answer student financial-aid questions; a recruiting team wants an AI tool to summarize interview notes; or a health-information publisher wants a retrieval assistant that drafts articles for editorial review. Do not pretend you are assessing a specific company’s undisclosed system. Say what is hypothetical, what is based on public information, and what assumptions you made.
A useful scenario brief includes
Purpose: the user problem and the decision the system influences.
People affected: direct users, people described in the data, and people who bear the consequences of a wrong output.
System boundary: model or vendor, inputs, integrations, human handoffs, and outputs.
Non-goals: what the system must not do and which decisions stay human-owned.
Assumptions: what you do not know but must temporarily specify to reason responsibly.
This is not busywork. A clear boundary prevents the most common personal-brand error in AI governance: making universal claims from a thin description. It also makes your work easier to discuss on LinkedIn, in an interview, or in a short newsletter. Instead of announcing that “AI needs guardrails,” you can share a particular decision and the reasoning behind it.
Build five proof assets, not one giant report
A 40-page PDF rarely earns attention. Five small, linked artifacts are easier to inspect, update, and repurpose. The UK government’s portfolio of AI assurance techniques is a useful reminder that assurance is a collection of practices, not a single document. For a personal AI governance portfolio, build a compact evidence trail.
1. A one-page system inventory
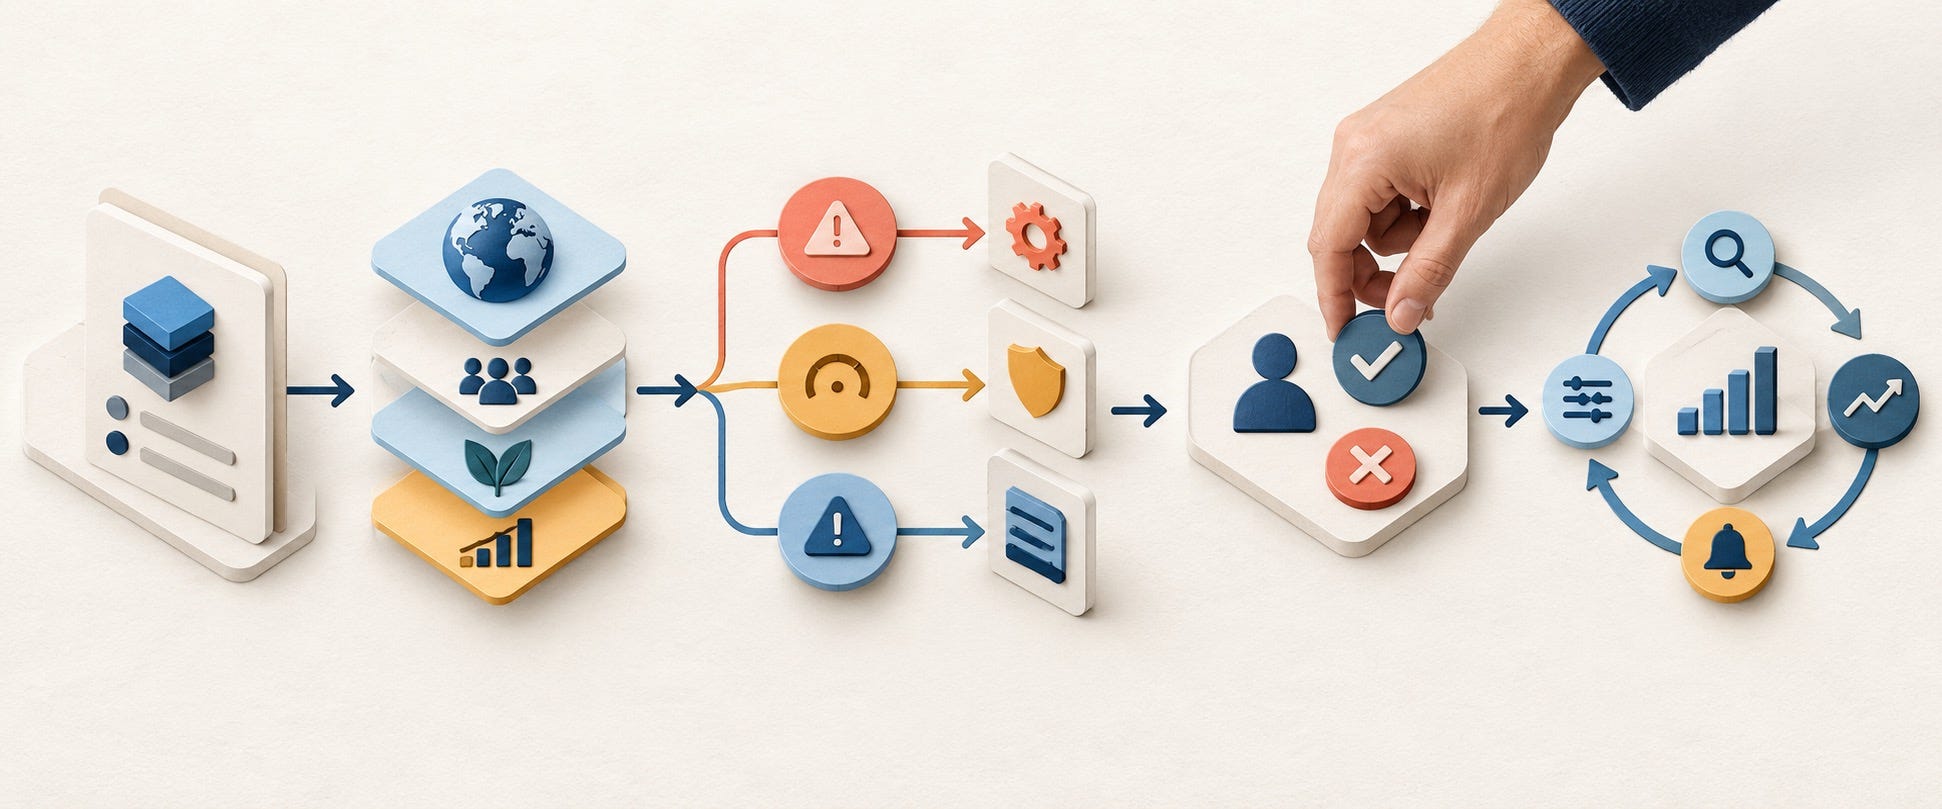
Describe the use case, owner, model or provider, data categories, users, geography, integrations, and lifecycle stage. Add “unknown” where appropriate. An inventory proves you know that governance starts with knowing what exists—not with writing a policy after launch.
2. A focused impact assessment
Name three to five plausible harms. Avoid a vague catalogue of every AI risk. For the student-aid assistant, you might examine incorrect eligibility information, unequal access for people using assistive technology, exposure of sensitive financial information, and overreliance on confident-sounding answers. For each harm, state who could be affected and how you would look for it.
3. A risk-and-controls map
Connect each material risk to a practical control. A control could be restricted access, a human approval step, retrieval-source requirements, adversarial testing, logging, an escalation path, or a product constraint. The point is not to create a decorative spreadsheet. The point is to reveal whether the control fits the risk and whether someone owns it.
4. A decision record
Write down one difficult choice. Perhaps the team decides not to let the assistant give final eligibility determinations. Or it limits answers to cited source material and routes uncertain cases to trained staff. Record the alternatives, trade-offs, decision owner, and what evidence would cause a review. This is the artifact that makes your judgment visible.
5. A monitoring and incident sketch
Governance does not end at approval. Define a few signals: complaint themes, unsupported-answer rate, override patterns, access anomalies, or a drift in escalation volume. Then describe what happens when a threshold is crossed. Even a hypothetical runbook shows that you understand governance as a continuing responsibility.
Together, these assets answer the quiet questions behind a recruiter’s or client’s screen: Can this person find the boundary? Can they prioritize? Can they make accountability concrete? Can they show their work without exaggerating it?
Make the work public without making false claims
Public work does not need to expose confidential systems. In fact, governance professionals should be unusually careful about confidentiality, security, privacy, and legal advice. Use fictional or sanitized cases. Remove proprietary architecture details. Do not publish a client’s risk register, screenshots, prompts, data samples, or incident information. If you are sharing work derived from a real role, obtain the appropriate permission and talk about the method, not protected details.
Label every artifact with an evidence tag. “Scenario-based” means it is a structured hypothetical exercise. “Public-source analysis” means it draws from accessible material. “Project-derived, sanitized” means it reflects real work but has been generalized. Those labels do not weaken your portfolio. They make it safer to trust.
Use precise language: “I designed a scenario-based intake and risk-review flow” is stronger than “I built enterprise AI governance.” The first is verifiable. The second asks strangers to take you on faith.
Be equally careful with frameworks. You can say that an artifact was informed by NIST or OECD principles. Do not imply certification, legal compliance, or formal conformance unless you have the authority and evidence to make that statement. Governance is not only the subject of your work; it is the standard for how you describe your work.
Use AI as a reviewer, not as your authorial alibi
AI can make the portfolio faster to build, but it cannot make judgment appear where none exists. Use it to surface missing stakeholders, generate counterarguments, turn notes into a first draft, or ask where a control might fail. Then verify every claim and make the final calls yourself.
A simple review prompt can help you pressure-test a draft before you publish:
Act as a skeptical AI-governance reviewer. Read this scenario brief and return: (1) hidden assumptions, (2) affected groups I may have missed, (3) controls that do not clearly connect to a stated risk, (4) claims that overstate the evidence, and (5) three questions a decision-maker would ask before approving this use case. Do not invent facts; flag uncertainty.
Notice the instruction at the end. “Do not invent facts” is a small but important habit. The goal is not to get the model to bless your portfolio. The goal is to make your own review sharper. Keep a brief revision note when an AI critique changes your thinking. That is more interesting—and more credible—than claiming an AI-generated document is complete.
Turn each artifact into a visibility loop
One project can support several public touchpoints without becoming content sludge. Publish a concise case-study page as the canonical home. From it, create a short post about one decision, a newsletter note about one lesson, and a visual explainer showing one risk-to-control pathway. Link back to the full artifact for readers who want evidence.
The important constraint: vary the question, not the truth. A post can ask, “What should trigger human review?” A newsletter can explain why the system boundary came first. A conversation can focus on stakeholder ownership. All three should point to the same underlying scenario and carry the same evidence labels.
This is how a personal brand compounds. People begin to associate you with a way of working: specific, calm, useful, and honest about limits. In a noisy field, that association is more durable than a clever headline.
A 30-day build plan
In the first week, pick a scenario and write the one-page system inventory. In the second, conduct the focused impact assessment and create the risk-and-controls map. In the third, write a decision record and a lightweight monitoring sketch. In the fourth, ask two people from adjacent disciplines to review it: perhaps a privacy professional and a product lead, or a security practitioner and a researcher. Revise, label the evidence type, and publish the case study.
Do not wait for perfect scope. A small portfolio that shows real thinking is more useful than an ambitious framework diagram that never reaches a decision. The goal is not to look finished. The goal is to leave a trustworthy trail of how you approach uncertain work.
Frequently asked questions
What should an AI governance portfolio include?
Start with a bounded system inventory, a focused impact assessment, a risk-and-controls map, a decision record, and a monitoring or incident-response sketch. Each item should show assumptions, ownership, and evidence boundaries.
Can I build an AI governance portfolio without an AI governance job?
Yes. Use a realistic fictional scenario, public-source analysis, or approved sanitized work. Label scenario-based work clearly and never present it as operational experience you did not have.
Do I need an AI governance certification before I publish a portfolio?
No. A credential and a portfolio answer different questions. Study can be valuable, but publishing a bounded, well-labeled project lets people evaluate your reasoning directly. Do not imply that coursework equals formal certification or legal authority.
What are good AI governance portfolio projects for career switchers?
Choose a use case close to your existing expertise. A privacy professional might assess a consumer-support assistant; a product manager might map approval decisions for an internal copilot; a security professional might design access and incident controls for an AI workflow.
How do I share AI governance work without breaking an NDA?
Use fictional or sanitized cases, remove identifiable details, secure permission where needed, and focus on your method rather than confidential systems or outcomes. Never publish sensitive architecture, prompts, data, or incidents.
How can AI help with an AI governance portfolio?
Use AI to find blind spots, propose skeptical review questions, organize rough notes, and test clarity. Treat it as a critique partner, then verify facts and retain responsibility for the final analysis and claims.
Build the evidence before the label
AI governance needs people who can connect technology, risk, people, and practical decisions. You do not need to announce that you are the finished version of that person today. Build one honest scenario. Make the reasoning inspectable. Show what you know, what you assumed, and what you would test next. That is not a smaller personal brand. It is the kind that earns trust.
Further reading: NIST AI Risk Management Framework; UK Government: Portfolio of AI assurance techniques; OECD AI Principles.