


A visibility system for privacy engineers who want to be known for clear thinking, not for leaking the work they are paid to protect.
The goal is not to publish the private system. It is to teach the durable decision pattern.
The work that makes a privacy engineer valuable is often the work they are least free to publish. You see the data flow nobody diagrammed, question a collection field that “might be useful,” translate a legal requirement into a product constraint, or stop a risky idea before it becomes an incident. The details belong to users and to the organization. The judgment can still become part of your public reputation.
That distinction matters more now that AI can draft a polished post before your coffee cools. A fluent explanation is easy to generate. Trusted technical judgment is not. Your personal brand should make it easier for a hiring manager, collaborator, client, or future teammate to understand how you think when the answer is incomplete, the stakes are real, and public disclosure has limits.
This is not a guide to becoming a privacy influencer. It is a guide to building safe public proof: small, useful artifacts that demonstrate your reasoning without revealing a customer, internal architecture, security control, incident, or legal advice.
Your most credible content is not “here is what I built.” It is “here is how I framed a class of problem, what I protected, what trade-off I made, and what another team can learn from it.”
Why generic personal branding fails privacy engineers
Most branding advice tells you to share wins, case studies, behind-the-scenes work, and hot takes. That advice creates a conflict for privacy professionals. A useful story may contain data categories, vendor choices, threat assumptions, customer facts, internal disagreements, or details that make an attack easier. A dramatic “lesson learned” post can also turn a confidential event into a vague rumor that harms the people involved.
The opposite response—silence—is not ideal either. Privacy engineering is a cross-functional profession. The people who need to understand your value may not recognize it from a job title. They need evidence that you can connect product, legal, engineering, operations, and user trust. The IAPP’s definition of privacy engineering is broad for exactly this reason: the work spans system design, software, data science, infrastructure, processes, and user experience.
So replace the content question “What can I reveal?” with a better one: What reusable decision pattern can I teach without revealing the case that taught it to me?
The safe public-proof system
Build your public presence from a simple sequence: private work context, de-identified pattern, public evidence, practical teaching. The context stays private. The pattern becomes your contribution.
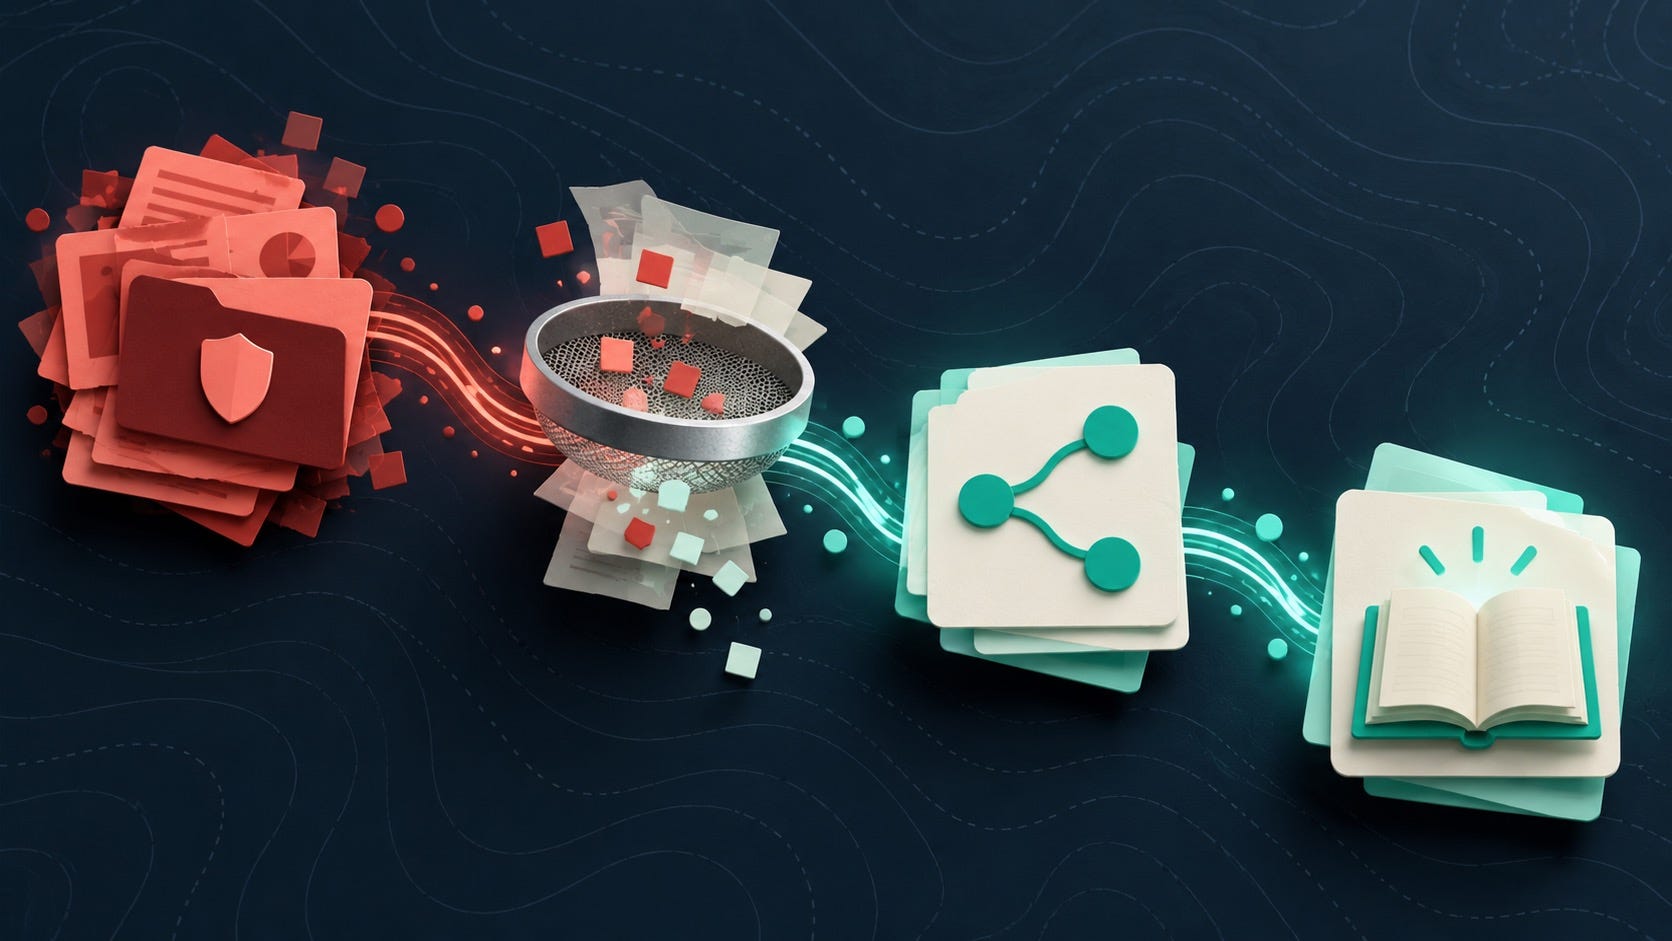
Filter the case, preserve the principle, then teach the pattern.
1. Capture the decision, not the dossier
After a meaningful piece of work, record a private note in plain language. Use four fields: the decision class, the privacy property at stake, the constraints, and the reasoning. Do not start with names, system screenshots, metrics, or a timeline of who said what. Start with the general problem.
For example, not: “We changed the onboarding flow for a named product after a particular complaint.” Instead: “When a product team wants to collect optional profile data early, how do we decide whether the timing and explanation support meaningful choice?”
2. Run a disclosure filter
Before anything reaches a public draft, remove five categories: identifiable people and organizations; exact data fields or volumes; internal tools, vendors, or architectures; unannounced roadmap information; and incident-specific sequences. Also remove claims that sound like legal advice, certification, or proof of compliance unless they are accurate, approved, and supportable.
Then ask a practical test: if a colleague who knows the original work reads this, could they reconstruct the project, customer, or weakness? If yes, abstract one level higher or do not publish it.
3. Ground the public lesson
A de-identified idea is still stronger when it is anchored in public material. Link your explanation to a NIST privacy-engineering concept, a regulatory guidance document, a public design pattern, a research paper, or a plainly labeled personal observation. This lets readers separate established guidance from your interpretation.
4. Teach a decision a reader can use
End with a small artifact: a set of questions for a product review, a red-flag list for an AI feature, a one-page data-flow review ritual, or an explanation a staff engineer can take into a planning meeting. The artifact is what turns visibility into service.
Three content formats that show judgment without oversharing
The trade-off note
Choose one recurring tension: personalization versus minimization, explainability versus data exposure, or speed versus consent clarity. Explain the two legitimate goals. State the questions you would ask. Describe a few possible safeguards. Do not pretend there is one universal answer. This format proves that you can make a decision legible.
The privacy pattern explainer
Take a public concept—data retention, deletion, purpose limitation, access controls, or model-evaluation data—and translate it for one audience. A product manager needs a planning lens. An engineer needs an implementation conversation. A leader needs a consequence and a decision. Repeated explainers build a recognizable niche around useful translation.
The question set
Questions are excellent career proof because they show where your attention goes. A short post titled “Seven questions to ask before an AI feature touches customer content” can be more credible than a grand claim about responsible AI. Readers can use it immediately, and you do not need to imply that you have seen every answer.
Use AI as a bounded editor, not an authority
AI can make this system faster, but it can also create the exact risk you are trying to avoid: it may invent a confident claim, flatten the nuance, preserve a detail you meant to remove, or turn a careful lesson into generic “thought leadership.” Treat it as a drafting environment with a defined input boundary.
First, provide the model only a sanitized decision pattern. Never paste a ticket, customer story, raw data flow, private policy, source code, incident report, or meeting transcript into an unapproved tool. Second, instruct it to label assumptions, avoid legal conclusions, and produce questions rather than verdicts. Third, verify every factual statement against a public source before publishing.
Here is a safe starting prompt after you have completed your own redaction pass:
You are an editorial assistant for a privacy engineer. Turn the sanitized decision pattern below into a 500-word teaching note for product and engineering leaders. Keep the original principle and uncertainty. Do not add examples, statistics, regulations, company names, or technical details that are not supplied. Do not give legal advice. Include: the decision tension, five review questions, and one sentence that distinguishes public guidance from practitioner judgment. Flag any sentence that makes an unsupported claim.

Sanitized pattern: [paste only de-identified, non-confidential material]
That last instruction—flag unsupported claims—is a differentiator. It makes the human reviewer’s job visible in the final quality, even if readers never see the prompt.
Build a profile that makes your lane obvious
A privacy engineer’s profile does not need a long tool list or a slogan about “passion.” It needs a specific promise. Try this structure: I help [team type] make [decision class] safer by translating [privacy concern] into [practical engineering or product outcome].
For example: “I help product and engineering teams turn data-use questions into understandable design choices, with privacy built into the work instead of bolted on at the end.” This is a direction, not a claim of universal expertise. Follow it with public evidence: two explainers, a reading list with your notes, a conference recap, a responsible AI question set, or a small open-source contribution where the scope is truly public.
Choose one home base—a simple site, LinkedIn, or Substack—and one distribution channel. The point is recognition, not omnipresence. A reasonable cadence is one durable teaching artifact every two to four weeks, plus occasional notes on public developments you have actually read.
Make collaboration part of the brand
Privacy engineering is rarely a solo performance. Your content should show that. Describe how you would invite product, legal, security, accessibility, data, and support partners into a decision. Credit public research and fellow practitioners. Ask for counterexamples. When someone corrects an oversimplification, update the post instead of defending the first draft.
Visible judgment includes knowing when a decision needs more than one discipline.
This approach has a quiet advantage. It tells future collaborators that you are not building an audience at their expense. You are building a body of work that makes their next conversation easier.
A 30-day start without a content machine
Week one: Write a private inventory of ten decision classes you encounter repeatedly. Do not write cases; write categories.
Week two: Pick one category with a public source you can read closely. Draft ten reader questions before asking AI for help.
Week three: Create one 600-word pattern explainer. Run the disclosure filter, source check, and a colleague review if appropriate.
Week four: Publish it, then turn the best question in the comments into the next artifact. Update your profile with the lane you are beginning to occupy.
Do not measure success by impressions alone. A better signal is whether the right people can now describe what you are good at: “They make privacy decisions understandable,” “They catch the question we missed,” or “They know how to keep a product move useful without making it reckless.” That is a reputation worth compounding.
FAQ: Privacy engineer personal branding
What should a privacy engineer post about?
Post de-identified decision patterns, public privacy concepts translated for a practical audience, review questions, and carefully sourced observations. Avoid customer stories, unannounced work, internal diagrams, incident details, and claims you cannot support publicly.
Can privacy engineers use AI for personal branding?
Yes, as a bounded editor. Give it only sanitized material, prohibit invented facts and legal conclusions, require it to flag assumptions, and verify the final draft yourself. Never use an unapproved AI tool as a destination for confidential work.
How do I build a privacy engineering portfolio if my work is confidential?
Build a portfolio of reasoning, not client artifacts. Publish explainers, question sets, public-source annotations, small educational templates, or open work with genuinely public scope. Show how you frame trade-offs and validate claims.
Do I need to use my real name to build a professional presence?
Not always. A consistent professional identity can work for some goals, but real-name visibility may be necessary for certain career paths. Decide based on your risk tolerance, employer policy, and the type of trust you want to build; do not let generic branding advice make that decision for you.
How often should a privacy engineer publish content?
One useful, reviewed artifact every two to four weeks is enough to start. The standard is not volume; it is accuracy, safety, and a clear benefit to the reader.
How can I avoid sounding like an AI-generated privacy influencer?
Use specific questions, state uncertainty, cite public sources, include the trade-off, and remove sweeping claims. Let AI help shape the draft, but keep the final judgment, examples, and responsibility human.
Useful public starting points: NIST Privacy Engineering Program; IAPP’s definition of privacy engineering; USENIX privacy-engineering career guidance. These sources provide background; they do not replace organizational policy, legal counsel, or security review.